Anatomy of a Bust: The Digital Trail That Brought Down a Ransomware Empire
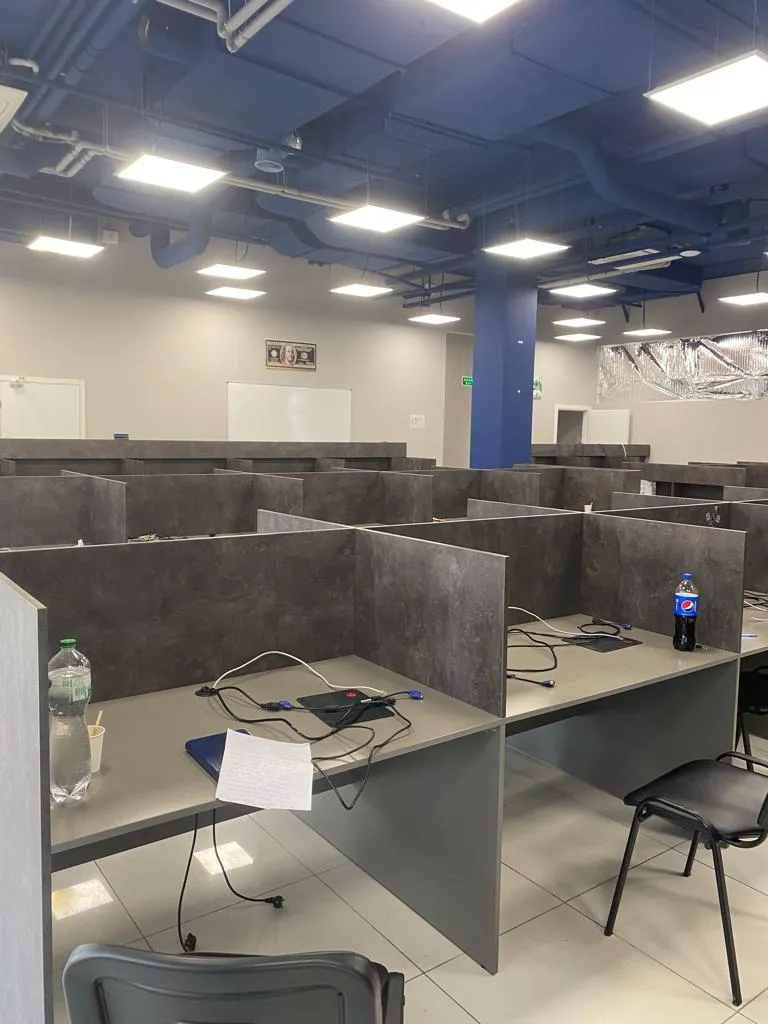
Photo: National Police of Ukraine / Ministry of Internal Affairs of Ukraine, CC BY 4.0, via Wikimedia Commons
On February 19, 2024, visitors to LockBit's dark web leak site were greeted with something the group's operators had never anticipated: a seizure banner bearing the logos of the FBI, the UK's National Crime Agency, Europol, and law enforcement agencies from nine other countries. The message was unambiguous. The infrastructure was gone. The administrators were identified. The empire, painstakingly constructed over four years of extortion campaigns that netted an estimated $1 billion from victims worldwide, had been dismantled from the inside.
Operation Cronos, as the coordinated takedown was designated, did not happen overnight. It was the culmination of an investigation that threaded together blockchain analytics, server infiltration, human intelligence, and the kind of methodical digital forensics that ransomware operators consistently underestimate. Understanding how it unfolded offers a rare window into the investigative machinery that authorities deploy against the most sophisticated cybercriminal organizations operating today.
Who Was LockBit?
LockBit emerged around 2019 as a ransomware-as-a-service (RaaS) operation — a business model in which a core development team creates and maintains the malware and supporting infrastructure, then licenses it to a network of affiliates who conduct the actual intrusions. The affiliates keep a portion of each ransom payment, typically around 80 percent, while the core group collects the remainder. This arrangement allowed LockBit to scale aggressively without exposing its developers to the operational risks of direct attacks.
By 2022, LockBit had become the most deployed ransomware variant globally, according to the Cybersecurity and Infrastructure Security Agency (CISA). Its victims ranged from hospital systems and school districts across the United States to industrial firms, law offices, and government contractors in dozens of countries. The group operated with a notable degree of professionalism, maintaining a public-facing "customer service" portal for ransom negotiations and even running a bug bounty program that paid researchers to identify flaws in its own software.
The Investigative Architecture
The investigation that became Operation Cronos was not launched by a single agency. It grew from parallel inquiries across multiple jurisdictions that gradually converged. The FBI's cyber division, working in coordination with the NCA and Europol's European Cybercrime Centre (EC3), began pooling intelligence on LockBit infrastructure as early as 2022.
A central pillar of the investigation was cryptocurrency tracing. Ransomware operations live and die by their ability to receive and launder cryptocurrency payments without exposing the identities of their operators. LockBit used a network of cryptocurrency wallets and mixing services designed to obscure the flow of funds. However, blockchain analysis firms working with law enforcement — including Chainalysis, which has supported numerous ransomware investigations — were able to map transaction patterns across the Bitcoin and Monero blockchains, identifying clusters of wallets associated with LockBit ransom payments and tracing proceeds as they moved through exchanges and over-the-counter brokers.
Several of those exchanges were operating in jurisdictions with cooperative law enforcement relationships. When investigators served legal process on those platforms, transaction records revealed identifying information — IP addresses, account details, and in some cases, direct links to banking infrastructure — that helped build profiles of specific affiliates and, ultimately, members of the core team.
Infrastructure as Evidence
Perhaps the most significant breakthrough in Operation Cronos was the infiltration of LockBit's own servers. According to statements from the NCA and the U.S. Department of Justice, investigators gained access to LockBit's backend infrastructure, including the affiliate panel through which partners managed their campaigns, the decryption keys the group held over victims, and internal communications.
This access was not announced until the moment of the public takedown — a deliberate strategy that allowed investigators to observe the operation in real time, collect evidence, and identify affiliates without alerting the group's leadership. The DOJ noted that the infiltration yielded over 1,000 decryption keys, which were subsequently made available to victims through the FBI and partner agencies.
The server access also exposed a fundamental operational security failure: LockBit's infrastructure was more centralized than the group's leadership apparently realized. Despite presenting itself as a distributed, resilient criminal enterprise, key components of its backend were concentrated in ways that made simultaneous seizure possible. Law enforcement agencies executed server takedowns across the United States, the United Kingdom, Germany, France, Finland, the Netherlands, Australia, and Japan in a coordinated sequence timed to prevent the group from migrating or destroying evidence.
Unmasking the Administrator
The most consequential moment of Operation Cronos was the public identification of LockBit's alleged primary administrator. Russian national Dmitry Yuryevich Khoroshev, operating under the alias "LockBitSupp," was named in indictments unsealed by the DOJ in May 2024 and sanctioned by the U.S. Treasury's Office of Foreign Assets Control. The State Department announced a reward of up to $10 million for information leading to his arrest.
Khoroshev's identification was the product of multiple converging investigative threads. His online persona, LockBitSupp, had been active across cybercriminal forums for years, and investigators were able to correlate communication patterns, technical artifacts, and financial flows across those interactions. Crucially, investigators found that Khoroshev had made a series of operational security errors over the years — using email addresses and cryptocurrency wallets that, when traced across different contexts, created linkages his persona was designed to prevent.
This pattern — the gradual erosion of anonymity through accumulated small mistakes — is consistent with how law enforcement has unmasked dark web operators in numerous prior cases. Maintaining perfect operational security over years of activity, across dozens of platforms and thousands of transactions, is extraordinarily difficult. Investigators are patient; they archive data and wait for correlations to emerge.
What Operation Cronos Teaches Us
The LockBit takedown illustrates several principles that define modern cybercriminal investigations. International coordination is now a baseline requirement: no single agency has the jurisdiction or technical reach to dismantle a multinational operation alone. The Five Eyes intelligence alliance and formal frameworks like the Budapest Convention on Cybercrime have made cross-border evidence sharing faster and more reliable than ransomware operators typically account for.
Blockchain's reputation for anonymity continues to be overstated. While privacy-focused cryptocurrencies and mixing services add friction to financial tracing, they do not provide the impenetrable anonymity that many criminal operators assume. The ledger is permanent, and blockchain analysis capabilities improve continuously.
Perhaps most importantly, operational security failures remain the most reliable path to attribution. LockBit's leadership ran a sophisticated criminal enterprise for years, yet the investigation found persistent gaps between the group's public posture of invulnerability and the actual security practices of its operators. Those gaps, accumulated over time, provided investigators with the footholds they needed.
For ransomware groups still operating, Operation Cronos was intended as a message as much as a law enforcement action. The NCA and FBI made that explicit, publishing personal details about Khoroshev and replacing LockBit's leak site with a resource for victims — a deliberate act of psychological disruption designed to corrode trust within the criminal ecosystem that sustained the group. Whether that message reshapes the ransomware landscape in any lasting way remains to be seen. But the investigation itself stands as a detailed record of what it takes to bring a billion-dollar cybercriminal operation to account.