Face Value: When the Executive on Your Screen Is a Synthetic Imposter
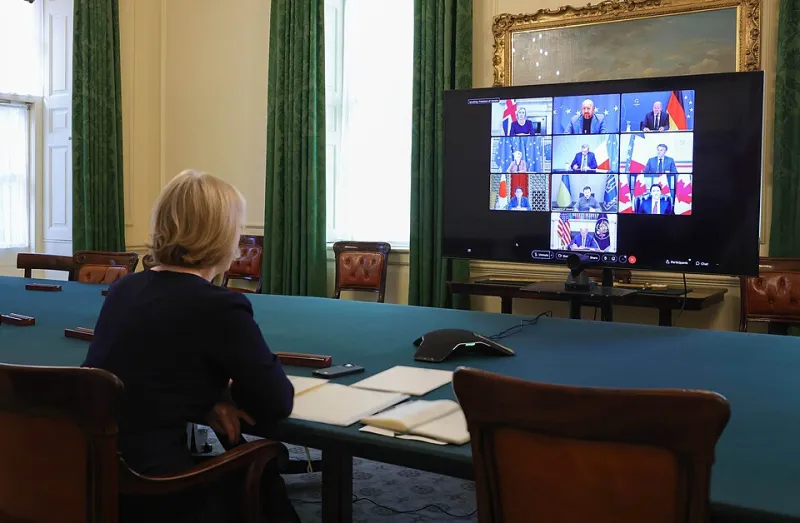
Photo: Number 10, CC BY 2.0, via Wikimedia Commons
The video call looked entirely routine. A mid-level finance employee at a multinational firm joined what appeared to be an urgent, executive-convened meeting. The CFO was on screen. So were several other recognizable colleagues. The instructions were clear: process a wire transfer immediately, and keep the matter confidential until further notice.
The CFO, of course, had never scheduled the meeting. Every face on that call had been fabricated by artificial intelligence. By the time the fraud was confirmed, $25 million had left the company's accounts — a figure that became one of the most widely cited examples of deepfake-enabled financial fraud when Hong Kong authorities disclosed it in early 2024.
This is no longer a theoretical threat. It is an operational one, and it is evolving faster than most organizations' defenses.
What Deepfake Recruitment and Executive Fraud Actually Look Like
The term "deepfake recruitment scam" has come to describe two related but distinct attack patterns. In the first, threat actors impersonate corporate executives — typically a CEO, CFO, or CISO — during video calls or in pre-recorded messages to pressure employees into credential disclosure or unauthorized financial actions. In the second, criminals pose as legitimate employers during remote job interviews, using synthetic video to deceive candidates into submitting sensitive personal data, installing malicious software under the guise of onboarding tools, or accepting fraudulent employment that serves as a money-mule pipeline.
The FBI's Internet Crime Complaint Center (IC3) issued warnings about both variants, noting that complaints involving deepfake video in hiring contexts increased meaningfully in recent years. In those cases, applicants reported that interviewers' lip movements were visibly out of sync with their audio — a telltale artifact that, when noticed, exposed the deception.
But detection is not always that straightforward. The quality ceiling for synthetic video is rising sharply, and the cost floor is dropping just as fast.
The Technical Barrier Has Collapsed
Three years ago, producing a convincing real-time deepfake required significant computational resources and specialized expertise. Today, commercially available tools — some marketed entirely legally for entertainment and content creation — have reduced that barrier dramatically. An attacker with a modest GPU, publicly available source footage of a target executive, and one of several open-source or low-cost face-swap applications can generate a usable synthetic video in hours.
For high-value targets, threat actors invest more. They scrape earnings call recordings, conference keynotes, LinkedIn video posts, and media interviews to build training datasets that capture a subject's facial geometry, vocal patterns, and characteristic mannerisms. The resulting output can be startlingly convincing under the compressed visual fidelity of a standard video-conferencing platform — which itself obscures many of the artifacts that would betray a synthetic face in high-resolution conditions.
Cybersecurity researchers at organizations including Mandiant and Recorded Future have documented threat groups incorporating deepfake capabilities into broader business email compromise (BEC) frameworks, treating synthetic video as a force multiplier for campaigns that previously relied solely on spoofed email addresses and social engineering scripts.
Documented Cases and the Anatomy of the Attack Chain
Beyond the Hong Kong incident, law enforcement disclosures and corporate breach notifications have outlined a recognizable attack chain. It typically begins with open-source intelligence gathering — the attacker identifies a target organization, maps its executive hierarchy using LinkedIn and press coverage, and selects an employee with financial authority or privileged system access as the victim.
A pretext is constructed, usually invoking urgency: a regulatory deadline, an acquisition under NDA, a security incident requiring immediate credential resets. The victim receives a calendar invitation from a spoofed or compromised email address, joins a video call, and encounters the synthetic executive. In some documented variants, the deepfake is accompanied by real human co-conspirators who handle portions of the conversation that the AI cannot navigate in real time.
The FBI's 2023 and 2024 public advisories specifically flagged the use of AI-generated profile photos and video in fraudulent job applications targeting remote positions with access to sensitive systems or financial infrastructure — a vector that HR departments have been slow to account for.
Detection Strategies: What Individuals and Organizations Can Do
No single countermeasure eliminates deepfake risk, but a layered approach substantially reduces exposure.
Establish out-of-band verification protocols. Any request for credential sharing, financial authorization, or sensitive data disclosure — regardless of how it arrives — should be confirmed through a separate, pre-established communication channel. Call the executive's known direct line. Do not use contact information provided within the suspicious communication itself.
Train employees to recognize deepfake artifacts. While artifact quality varies, common indicators include unnatural blinking patterns, lighting inconsistencies at the hairline and ear boundaries, subtle geometric distortions when the subject turns their head, and audio-visual synchronization failures. Security awareness programs should include video examples of these artifacts so employees can recognize them under pressure.
Implement behavioral and contextual skepticism. Legitimate executives operating within established organizational processes rarely demand secrecy, bypass normal approval chains, or inject extreme urgency into routine financial or access-related requests. These social engineering hallmarks remain consistent whether the delivery mechanism is email, voice, or synthetic video.
For HR departments specifically: Require live, interactive elements during remote hiring processes that are difficult to sustain with pre-generated or looped synthetic video. Ask candidates to perform unrehearsed physical actions — holding up a handwritten word, rotating their face at an unusual angle — that expose the limitations of real-time face-swap technology.
Invest in detection tooling, with appropriate skepticism. Several vendors offer deepfake detection software, and some video-conferencing platforms are beginning to integrate authenticity signals. These tools are imperfect and should be treated as one layer among many, not a definitive solution.
The Organizational Posture Problem
Perhaps the most consequential vulnerability is not technical but procedural. Organizations that have not explicitly updated their financial authorization and credential-management policies to account for synthetic media remain exposed regardless of how much security software they deploy. A wire transfer that requires three email approvals but can be initiated by a single video call has a policy gap that deepfake technology is purpose-built to exploit.
The IC3 recommends that businesses adopt multi-person authorization requirements for all significant financial transactions, enforce strict callback verification for any executive-initiated request that departs from standard procedure, and conduct regular tabletop exercises that include synthetic-media attack scenarios.
The technology driving these attacks will not become less sophisticated. The organizations that weather this threat will be those that treat procedural discipline and human judgment as security controls in their own right — because when the face on the screen cannot be trusted, the process behind the screen must be.